7 Layers of Cybersecurity Manufacturers Should Evaluate to Protect Their Business and Operations
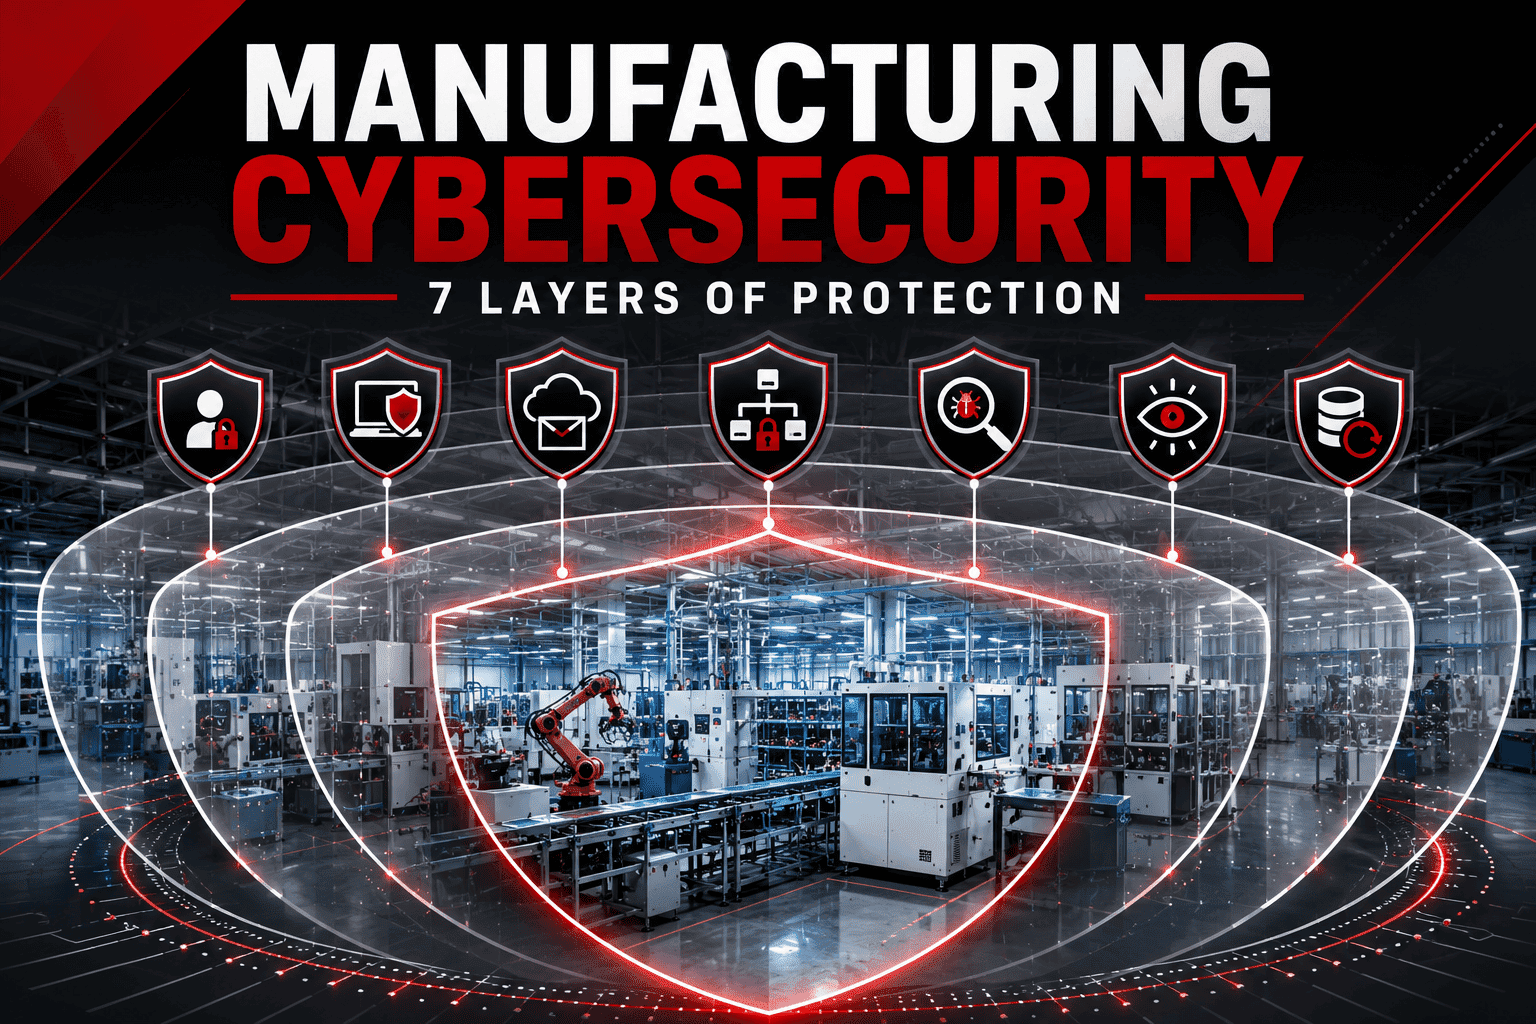
Manufacturers generally need cybersecurity controls across seven layers: identity and access, endpoints, email and cloud services, networks and IT/OT connections, vulnerability management, 24/7 detection and response, and backup and recovery.
The depth of those protections should reflect the manufacturer’s size, technology environment, data, customer requirements, compliance obligations, and the operational impact of a cyber incident. A 40-person machine shop and a 400-person manufacturer with multiple facilities may use many of the same security principles, but the way those controls are implemented can be very different.
A useful way to evaluate manufacturing cybersecurity is through four outcomes:
PREVENT → DETECT → RESPOND → RECOVER
No single cybersecurity product accomplishes all four. Manufacturers need multiple layers that work together so that when one control fails, another can help identify, contain, or recover from the incident.

1. Identity and Access Security
User accounts are one of the primary ways employees, vendors, and applications access company systems. Manufacturers need controls that reduce the likelihood that a stolen password or unnecessary account becomes an entry point into the environment.
Multi-factor authentication (MFA) should be used wherever practical for important business systems, particularly Microsoft 365, cloud applications, remote access, administrative accounts, and other externally accessible services.
Account management matters as well. Former employees should not retain access after leaving the company. Administrative privileges should be limited to people who require them. Shared and generic accounts should be reduced where possible because they make it harder to determine who performed an action.
Manufacturing environments also need to account for vendor access. Equipment manufacturers, integrators, and other third parties may require remote access to specialized systems. Those connections should be controlled rather than remaining permanently available with shared credentials.
For manufacturers subject to CMMC, NIST SP 800-171, customer security requirements, or cyber insurance requirements, identity controls may also be contractual or compliance considerations.
2. Endpoint Protection
Workstations, laptops, and servers create another major layer of the security environment.
Traditional antivirus remains useful, but modern endpoint protection can provide broader visibility into suspicious activity. Endpoint Detection and Response (EDR) and related technologies can identify behaviors that may indicate malware, ransomware, credential theft, or other malicious activity.
Manufacturers should know which endpoints are being protected and monitored.
That sounds simple, but it becomes more difficult when an organization has multiple facilities, remote employees, engineering workstations, shared production computers, servers, and older systems. An endpoint that isn’t included in the security program can create a visibility gap.
AT-NET’s managed cybersecurity approach includes endpoint security as part of a broader security program rather than treating antivirus as the entire cybersecurity strategy.
3. Email and Cloud Security
Email remains closely connected to identity, data, and business communications, making it an important part of a manufacturer’s security program.
A compromised Microsoft 365 account, for example, can potentially expose email, files, contacts, and other cloud resources available to that user. Attackers may also use compromised accounts to send convincing messages to customers, vendors, or other employees.
Manufacturers should combine MFA with appropriate email filtering, account protection, access controls, and monitoring.
Cloud applications need similar attention. Moving an application or data to the cloud changes where the technology is hosted, but the manufacturer still needs to consider who can access it, how accounts are protected, how threats are monitored, and how important data can be recovered.
AT-NET’s cloud cybersecurity services include Microsoft 365 security, cloud risk assessments, access controls, 24/7 threat monitoring, compliance management, and incident response and recovery.
4. Network and IT/OT Security
Manufacturing networks can include corporate IT, production-related systems, industrial equipment, IoT devices, cameras, access-control systems, wireless networks, vendor connections, and other connected technology. Those systems should not automatically have unrestricted access to one another.
Network security can use firewalls, segmentation, access policies, secure remote connectivity, and monitoring to control how systems communicate. This becomes particularly important where IT and operational technology (OT) intersect.
An employee clicking a malicious email attachment on the corporate side of the business should not automatically give an attacker unrestricted access to every connected production system.
The same principle applies to vendors. A third-party technician who needs access to one piece of equipment doesn’t necessarily need broad access to the rest of the corporate network. Manufacturers should document important IT/OT connections and determine which communications are actually required for operations.
Legacy production systems can make this more complicated. Some equipment may rely on older software or operating systems that cannot be patched or replaced without significant operational consequences. Segmentation, access restrictions, and monitoring can become especially important when the underlying system cannot be secured in the same way as a modern workstation or server.
5. Vulnerability and Patch Management
Security vulnerabilities are continuously discovered in operating systems, applications, network equipment, and other technology.
Manufacturers need a repeatable process for identifying those vulnerabilities and determining which ones require attention. Patch management is part of that process, but vulnerability management is broader.
A vulnerability-management program should help the organization understand:
- What assets exist
- Which vulnerabilities affect those assets
- How serious the vulnerabilities are
- Whether the affected system is exposed
- What business function the system supports
- Whether a patch or other remediation is available
- How remediation should be prioritized
Manufacturing environments may require additional planning because some systems cannot simply be rebooted during production. A critical production-supporting system may require a scheduled maintenance window. A legacy application may not support the latest operating-system version. Specialized equipment may require coordination with the equipment vendor before changes are made.
That doesn’t eliminate the vulnerability. It means remediation needs to account for both cybersecurity risk and operational risk.
AT-NET’s managed cybersecurity services include vulnerability management as part of its approach to identifying and addressing security weaknesses.
6. 24/7 Detection and Response
Preventive controls will not stop every attack.
Manufacturers need the ability to identify suspicious activity when someone bypasses an existing control.
Managed Detection and Response (MDR), Extended Detection and Response (XDR), security monitoring, and incident response services can provide visibility into activity occurring across endpoints, identities, networks, cloud systems, and other parts of the environment.
The value comes from more than generating alerts. Someone needs to evaluate those alerts and determine whether action is required. That is particularly important outside normal business hours. Manufacturing operations may run second or third shifts, and cyberattacks don’t follow the company’s office schedule.
AT-NET provides 24/7 monitoring and incident response as part of its managed cybersecurity services. AT-NET reports an average incident response time of under 60 seconds for its cloud cybersecurity services.
For manufacturers, the objective is to reduce the amount of time malicious activity can continue without investigation or response.
7. Backup and Recovery
Cybersecurity planning needs to account for what happens when preventive and detection controls aren’t enough. Ransomware, malicious deletion, hardware failures, software problems, and human error can all create situations where systems or data need to be restored. Manufacturers should maintain backups based on the importance of their systems and the amount of data they can afford to lose.
For mission-critical information, AT-NET notes that backup frequency may need to be at least hourly, depending on the organization’s recovery requirements. Backup copies should also be protected.
Immutable storage prevents protected backup data from being changed during its defined retention period, providing another layer of defense if an attacker attempts to modify or delete recovery data.
AT-NET’s managed backup approach includes local and off-site backups, immutable storage, daily backup review, restores as needed, and disaster recovery support.
Recovery planning should then define which systems are restored first, how quickly they need to return, and who is responsible for the recovery process.
The Manufacturing Cybersecurity Stack
These seven security areas can be organized around four outcomes.
| Outcome | Examples of Controls |
|---|---|
| Prevent | MFA, access controls, email security, firewalls, segmentation, patching |
| Detect | EDR, MDR/XDR, vulnerability management, 24/7 monitoring |
| Respond | Alert investigation, containment, incident response, remediation |
| Recover | Immutable backups, off-site backups, restores, disaster recovery planning |
A strong security program doesn’t depend entirely on one outcome.
Prevention reduces the likelihood of a successful attack. Detection helps identify activity that gets through. Response limits the impact of an incident. Recovery provides a path back to operations when systems or data are disrupted.
Does Every Manufacturer Need the Same Cybersecurity?
No. Cybersecurity should be proportionate to the organization’s risks and requirements.
Seven factors are particularly useful when determining the appropriate level of protection:
1. Company size
More users, endpoints, facilities, and systems generally create a larger environment to manage and secure.
2. IT environment
The number and complexity of servers, networks, cloud applications, endpoints, and remote users affect security requirements.
3. OT environment
Connected production systems, legacy equipment, vendor access, and IT/OT convergence can create additional risks.
4. Data sensitivity
Manufacturers handling engineering information, intellectual property, employee information, customer data, or Controlled Unclassified Information may require stronger controls.
5. Customer and contractual requirements
Customers may impose cybersecurity requirements as a condition of doing business.
6. Compliance and insurance requirements
CMMC, NIST SP 800-171, cyber insurance policies, and other requirements may establish specific controls the organization needs to implement.
7. Operational impact
A company where an IT outage can quickly interrupt production has a different risk profile from an organization that can operate manually for an extended period.
These factors help determine how deeply each security layer needs to be implemented.
What Does a Practical Manufacturing Cybersecurity Program Protect Against?
Different controls address different types of risk.
| Security Area | Helps Address |
|---|---|
| MFA and identity security | Stolen credentials and unauthorized account access |
| Endpoint protection | Malware, ransomware, and suspicious endpoint activity |
| Email/cloud security | Phishing, account compromise, and cloud threats |
| Network and IT/OT security | Unauthorized access and movement between systems |
| Vulnerability management | Known security weaknesses |
| 24/7 monitoring | Threats that bypass preventive controls |
| Backup and recovery | Data loss and operational disruption |
The layers are most effective when they work together.
For example, MFA may prevent an attacker from using a stolen password. If the attacker reaches an endpoint another way, endpoint detection may identify suspicious behavior. Network segmentation can limit where the attacker can move. 24/7 monitoring can trigger investigation and containment. Protected backups provide a recovery option if systems are ultimately affected. That is the value of layered cybersecurity.
Cybersecurity Tools Still Need People and Processes
Technology alone doesn’t create a complete security program. Manufacturers also need people responsible for reviewing the environment, maintaining controls, responding to alerts, planning improvements, and helping leadership understand risk.
AT-NET’s managed IT clients receive a dedicated Technical Alignment Manager (TAM) and vCIO.
The Technical Alignment Manager helps keep the technology environment aligned with established technical standards and identifies areas that need attention. The vCIO helps leadership evaluate longer-term technology, cybersecurity, budgeting, risk, and business priorities.
AT-NET also operates an internally staffed 24/7/365 help desk with a response time of less than 60 seconds.
These functions address different needs. User support, technical alignment, cybersecurity monitoring, incident response, and strategic planning all contribute to maintaining a secure environment.
A 7-Point Manufacturing Cybersecurity Check
Manufacturing leaders can use seven questions to identify obvious gaps:
- Is MFA enabled for important cloud, remote-access, and administrative accounts?
- Are workstations, laptops, and servers protected and monitored?
- Are Microsoft 365, email, and cloud accounts included in the security strategy?
- Are important IT/OT connections and third-party remote-access paths controlled?
- Do we have a repeatable vulnerability and patch-management process?
- Is someone monitoring and responding to security events 24/7?
- Are critical backups protected, reviewed, and recoverable?
A “no” or “we aren’t sure” doesn’t automatically mean the organization needs to purchase another product, but identifies an area that should be evaluated based on business risk.
How Manufacturers Should Prioritize Cybersecurity Improvements
Trying to implement every possible cybersecurity control simultaneously can create unnecessary cost and complexity.
A practical improvement plan can use four steps:
1. Identify
Document important systems, users, data, IT/OT connections, remote access, cloud services, and regulatory requirements.
2. Assess
Compare existing protections against the organization’s risks and requirements.
3. Prioritize
Address the gaps that create the greatest combination of likelihood and business impact.
4. Improve
Implement the appropriate technical controls, processes, monitoring, documentation, and recovery capabilities.
Then repeat the process as the environment changes.
A manufacturer adding a facility, implementing a new ERP system, connecting production equipment, pursuing defense contracts, or moving applications to the cloud may create new security requirements that didn’t exist when the original cybersecurity plan was developed. Cybersecurity should therefore be treated as an ongoing business process rather than a one-time project.
How Much Cybersecurity Is Enough?
There isn’t a universal number of security products that makes a manufacturer secure.
A practical cybersecurity program should provide capabilities to prevent common attacks, detect suspicious activity, respond quickly when something happens, and recover critical systems and data when necessary.
For manufacturers, that generally means evaluating seven layers:
- Identity and access security
- Endpoint protection
- Email and cloud security
- Network and IT/OT security
- Vulnerability and patch management
- 24/7 detection and response
- Backup and recovery
The appropriate depth of each layer should reflect the manufacturer’s operations, systems, data, customers, compliance requirements, and downtime risk.
Final Thoughts
Manufacturing cybersecurity works best as a layered system rather than a collection of unrelated security products.
The Prevent → Detect → Respond → Recover framework gives leadership a straightforward way to evaluate whether the security program covers the full lifecycle of a cyber incident.
AT-NET supports manufacturers with managed cybersecurity services that include MFA, endpoint protection, MDR/XDR, vulnerability management, managed network security, cloud and Microsoft 365 security, 24/7 monitoring and incident response, immutable backups, and disaster recovery capabilities.
AT-NET has served businesses since 1999 and works with more than 75 manufacturing clients. Managed IT clients also receive a dedicated Technical Alignment Manager and vCIO to help connect day-to-day technical management with longer-term cybersecurity and technology planning.
The objective is not to deploy every security tool available, but to build enough layers that one compromised password, vulnerable endpoint, phishing email, or failed control does not automatically become a major manufacturing disruption.
FAQ
What cybersecurity does a manufacturing company need?
Most manufacturers should evaluate seven areas: identity and access security, endpoint protection, email and cloud security, network and IT/OT security, vulnerability management, 24/7 threat detection and response, and backup and recovery. The depth of each control should reflect the manufacturer’s specific risks and requirements.
Does a small manufacturer need 24/7 cybersecurity monitoring?
Company size alone doesn’t determine the need for continuous monitoring. Manufacturers should consider their operating hours, systems, data, customer requirements, compliance obligations, and the potential impact of an undetected cyberattack.
Is antivirus enough for a manufacturing company?
Antivirus addresses only part of the risk. Manufacturers should also consider identity security, MFA, email and cloud protection, network controls, vulnerability management, threat detection and response, and protected backups.
Why is MFA important for manufacturers?
MFA adds another verification step when users access protected systems. It can reduce the risk that a stolen password alone gives an attacker access to Microsoft 365, remote-access systems, cloud applications, or administrative accounts.
How should manufacturers protect IT and OT networks?
Manufacturers should identify IT/OT connections, control unnecessary communication between systems, secure vendor remote access, use appropriate firewalls and segmentation, and monitor important connections. Specific controls should reflect the production environment and equipment requirements.
How should manufacturers prioritize cybersecurity spending?
Start with business impact and risk. Identify critical systems, sensitive data, regulatory requirements, known vulnerabilities, and operational dependencies. Prioritize gaps where a successful attack would create the greatest combination of likelihood and business impact.
About AT-NET
AT-NET provides managed IT, cybersecurity, infrastructure, cloud, backup and disaster recovery, and strategic technology services for manufacturers throughout North Carolina, South Carolina, Florida, and Eastern Tennessee.
AT-NET helps manufacturers evaluate cybersecurity risk, implement layered protections, monitor threats, respond to incidents, protect critical data, and align security investments with business and compliance requirements.
Does Your Manufacturing Cybersecurity Cover All Seven Layers?
Cybersecurity gaps are easier to address before they become incidents. AT-NET can evaluate your existing environment, identify areas that need attention, and help prioritize security improvements based on your operations and risk.


